
Legal
GRM LAW
The firm runs intake, conflicts, trust oversight and AML/CTF from one portal.
Whole-tenant ICT, with Conditional Access across the firm from 23 October 2026.

Defensive and advisory
An inventory of your internet-facing assets, scheduled external scans, findings ranked on exploitation data, and a monthly written position on what to fix first.
Overview
Attack surfaces change between penetration tests. A subdomain stood up for a campaign, a database port opened for a one-off job, a certificate that lapsed on a system nobody remembers building: none of it appears in a report from months earlier.
Attack surface management is the standing discipline that keeps the inventory current, monitors it with scheduled scans, and turns the change since last period into a short list of things to fix.
Black Shard is an Australian software engineering and cybersecurity firm. The scanner is built and operated by the firm. For managed engagements, Black Shard engineers review the results and identify the changes that require action instead of sending an unfiltered scanner report. The service is delivered Australia-wide.
The work runs as a cycle: inventory, discovery, verification, prioritisation, change, remediation and evidence.
Inventory: every registered domain, subdomain, host, public IP address and certificate the business owns, with a named owner for each. Discovery: scheduled external scans that catalogue every exposed host and service and flag remote-access and database ports when they surface.
Verification: each finding checked against known CVEs, misconfigurations and TLS problems, and against default logins in deep scans you consent to. Prioritisation: findings ranked against CISA's Known Exploited Vulnerabilities catalogue and EPSS exploit probabilities. Change: each scan diffed against the last one so the report is a change list. Remediation: the fix scoped and, where you want it, carried by Black Shard engineers. Evidence: a dated position an insurer or a customer's security questionnaire can rely on.
Email authentication is checked over DNS as well: SPF and DMARC, including softfail and p=none policies that leave a domain open to spoofing. Where a gap matters, the route an attacker could take to reach it is expressed in MITRE ATT&CK terms.
Most exposure sits on assets nobody is watching: the staging copy of the site left reachable, the old marketing microsite still resolving, the SaaS trial that was given a subdomain and forgotten, the mail relay that predates the current provider.
A scan of the assets you know about misses them by definition, so the first deliverable is the inventory itself, built from registrar and DNS records, certificate logs and the scans, with the hostnames that appear in one source and not the others treated as the interesting ones.
Each asset gets an owner: a named person in a role who can approve a change to it, and who is asked the question when the scan finds something on it. An inventory without owners produces findings nobody closes. How we build one is set out in our guide to building an inventory of internet-facing assets.
The first period builds the baseline that every later scan is compared with. It runs in a fixed order, and the first written position marks the end of onboarding.
A raw scanner report ranks by CVSS, which measures how bad a flaw could be. Exploitation data shows whether anyone is using it.
Our scanning ranks against two exploitation signals instead: CISA's Known Exploited Vulnerabilities catalogue, which lists flaws confirmed exploited in the wild, and EPSS, which scores the probability a flaw is exploited in the next thirty days. A high-CVSS finding with no exploit activity sits below a moderate one that attackers are using this month.
Every finding carries one of four verdicts: OK, at risk, not assessed because a scan could not complete, or not observable from outside. Only the first is treated as a pass. A system the scan cannot see is reported as a gap in coverage, never assumed to be fine.
Vulnerability scanning is one input to attack surface management: the scan lists what it can detect on the assets it was pointed at.
Attack surface management adds the inventory in front of the scan, so the scan is pointed at everything, and the review behind it, so the output is a ranked change list with owners instead of a report the size of the footprint.
A penetration test is a different instrument. It establishes what an attacker can do with your systems in a bounded engagement, with a human working the findings together into a route. Attack surface management is the standing watch between tests that catches drift and known exploitable weaknesses as they appear. Most businesses that run one end up running both, and the engineers who read the scans here also run the firm's penetration tests, so a finding that warrants a deeper look is scoped by the same people.
A point-in-time report describes the attack surface on the day it ran.
Monitoring compares every scan with the last one, so what lands in your inbox is the change since the previous period and what it means: the host that appeared, the port that opened, the certificate that expired, the software version that moved onto the KEV list since last month.
The written position is short by design. What changed in the footprint since the last period. Which findings matter, ranked on exploitation data, with the ATT&CK route where one exists. What to fix first, with the owner and the change named.
What was fixed since last time and verified closed on the following scan. Which assets could not be assessed or observed, so the coverage gap is documented. Any decision the business needs to make, such as retiring an asset instead of patching it.
The position is written for the person who owns the risk, and the same document answers an insurer at renewal or a customer's security questionnaire without a rewrite.
The scanner marks a finding OK only once the scan has verified it. Where a scan cannot see a system or cannot complete against it, the verdict says so and is never treated as a pass.
Black Shard holds SMB1001:2026 Gold, issued by CyberCert. Its own estate is at Essential Eight Maturity Level 3, assessed September 2026.
For a managed engagement, Black Shard engineers read each period's results against what the business runs, identify the changes that require action, and write the position. The engineers who read the scans also run the firm's penetration tests, Azure and Entra ID reviews and remediation work, so where a finding needs closing the fix can be scoped by the same firm.
The engagement runs the same way wherever the business is based. Scoping, the periodic review and any follow-up conversation happen by email and video call, and the position carries the same review either way.
Scans run only against assets the business owns or is authorised to have tested, confirmed in writing at scoping.
Brisbane businesses that would rather sit across a table for the review have that option.
Cost follows what is in scope: the number of domains and hosts in the footprint, how many environments are run, and whether the engagement stops at reporting or extends to remediation.
A free 30-minute scoping call settles the footprint and the cadence, or a brief to info@blackshard.com.au with a rough shape of what you want watched starts scoping from the detail you have.
Legal
The firm runs intake, conflicts, trust oversight and AML/CTF from one portal.
Whole-tenant ICT, with Conditional Access across the firm from 23 October 2026.

Health
The clinical site and the practice’s ICT now sit with one team.
Hosting, ICT management and security now run under one ongoing engagement.

Property
Every valuation, from inspection to invoice, runs through The Den.
Reports, sketch PDFs and fees come from the same job record in The Den.
Product screens shown with sample data.
Launching 2027
Designed for Australian businesses with 1 to 200 devices.
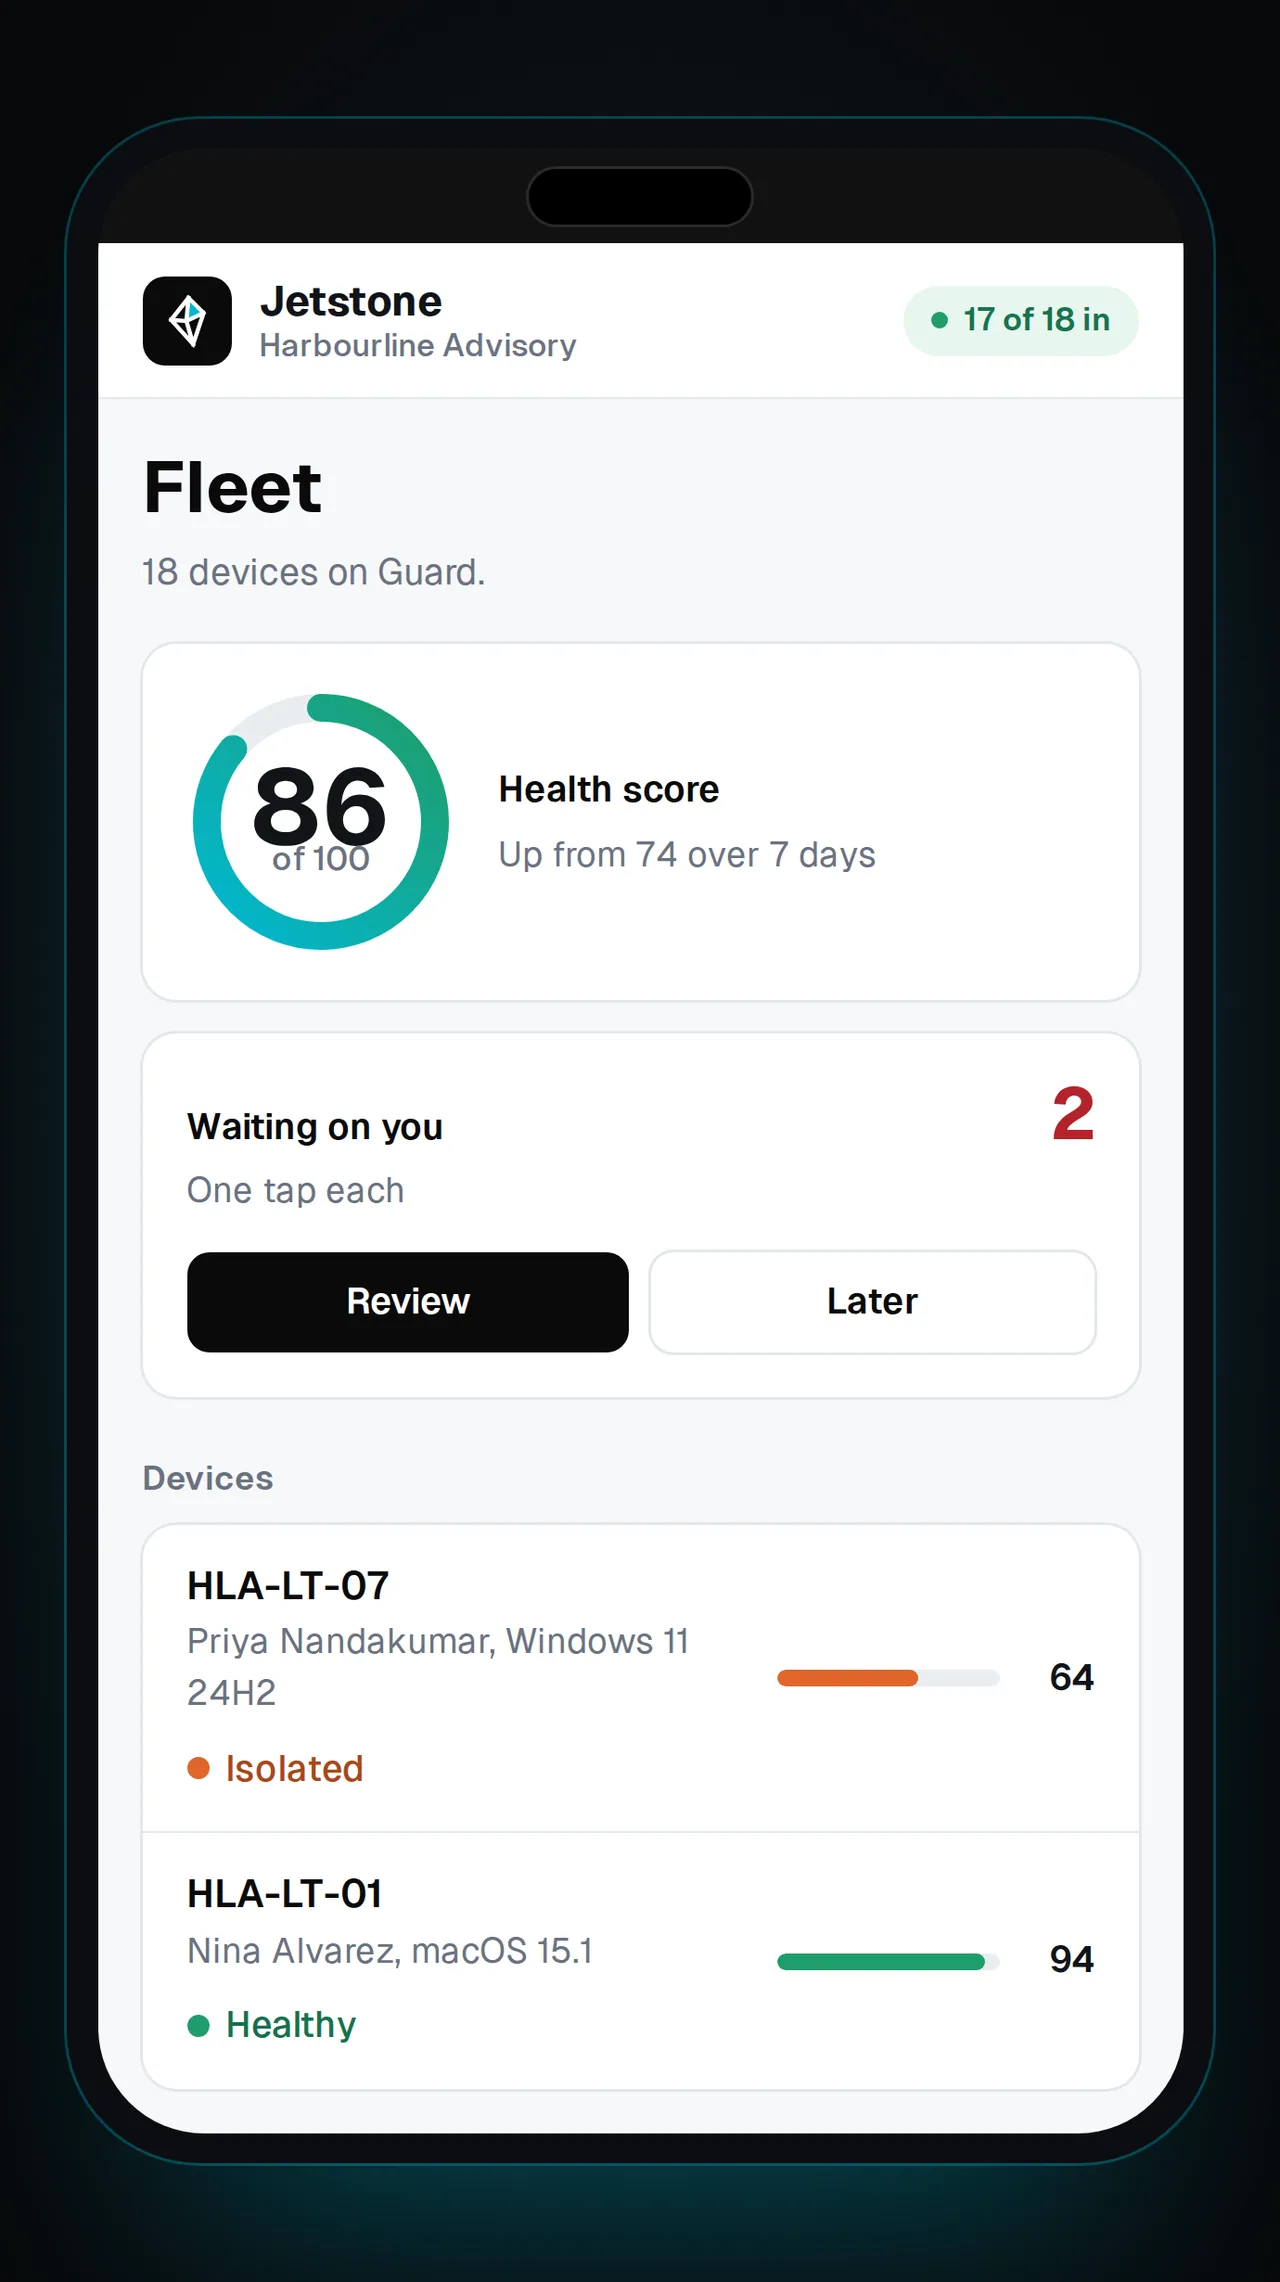
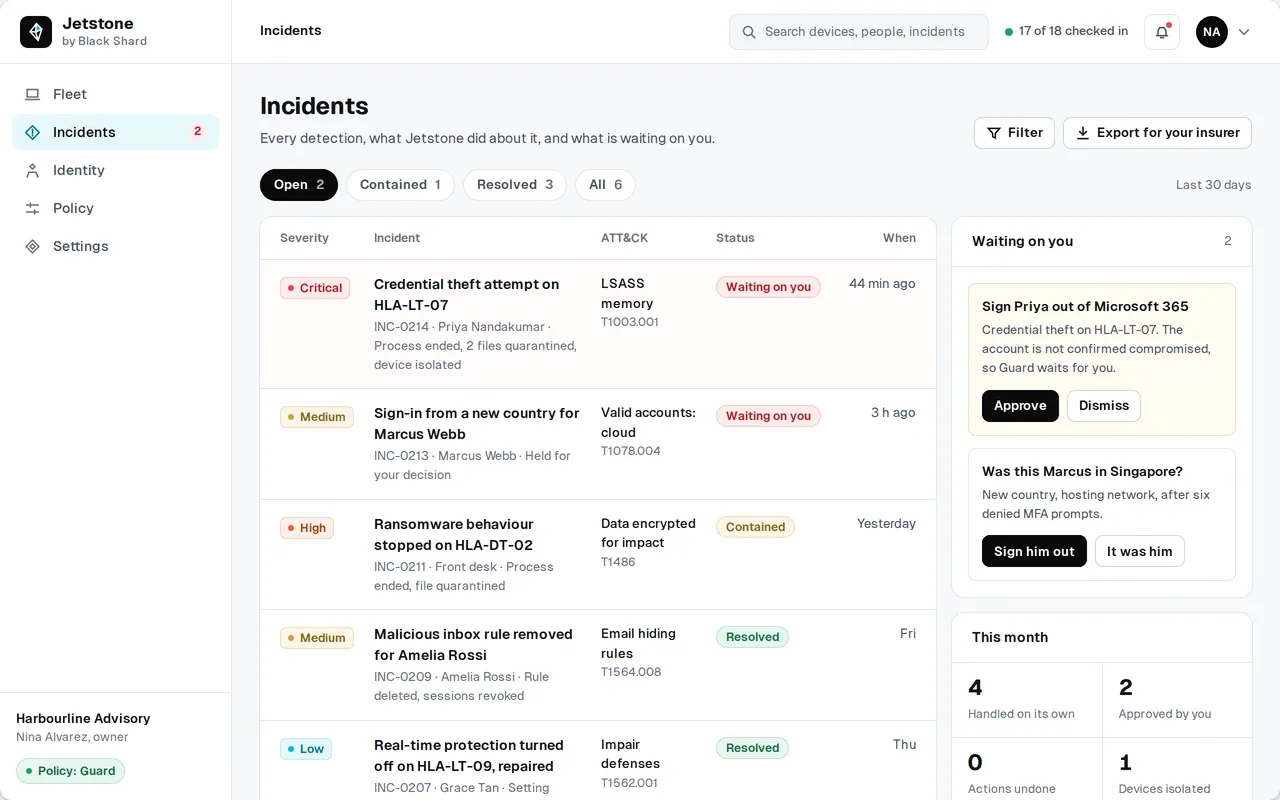
On a high-confidence detection, Jetstone is designed to act on its own against threats on a published list: end the process, quarantine the file, isolate the device, or sign the user out of Microsoft 365 or Google Workspace.
Identity watch will flag impossible travel, MFA fatigue, malicious inbox rules and risky OAuth consents.
Every automatic action will be undoable in one tap.
From the newsroom
 High severity
 Critical severity
An inventory of every internet-facing asset with a named owner, scheduled scans of that footprint, findings ranked on CISA KEV and EPSS exploitation data, change tracking between scans, a written monthly position on what to fix first. Remediation by Black Shard can be added where the engagement extends to it.
The standing discipline of knowing every asset your business exposes to the internet, scanning those assets on a schedule, ranking what the scans find on real exploitation data, and closing the findings that matter, with a written position each period on what changed. It differs from a one-off scan in the inventory in front of it and the review behind it.
A penetration test establishes what an attacker can do with your systems in a defined, bounded engagement. Attack surface management is the standing watch between tests: scheduled scans that catch drift and known exploitable weaknesses as they appear. Many businesses run both.
Vulnerability management works the list of flaws on the assets you already know about. Attack surface management starts one step earlier, with the inventory, so the assets nobody was tracking enter the list, and it ranks on exploitation data instead of severity alone.
Monitoring is the scheduled watch: scans of the external footprint, each compared with the last, so a new host, an opened port or an expired certificate shows up on the next scan. Management is the cycle around that watch: the inventory with a named owner for each asset, findings ranked on exploitation data, and each fix verified closed on the following scan. Black Shard runs both as one service.
On a schedule agreed at scoping, with change tracking that compares every scan against the one before it. The cadence depends on how much of the footprint changes and how quickly you need to know.
The registered domains and any known hosts, a named contact for each part of the business that owns internet-facing systems, and written authorisation to scan. No credentials and no agents on your systems: the scans run from outside, the way an attacker sees you.
Yes. The monthly written position is the standing rhythm. A finding that cannot wait is raised when it is found.
Yes. Where a finding needs closing, Black Shard can engineer the fix. Monitoring, penetration testing and remediation engineering run from the same firm.
The scan could not see the system from outside, or could not complete against it. Neither is treated as a pass. The verdict records the gap in coverage instead of assuming the system is fine.
Yes. Black Shard is an Australian firm and delivers Australia-wide; the service runs the same way regardless of where the business is based. Brisbane businesses can choose an in-person review.