
Legal
GRM LAW
The firm runs intake, conflicts, trust oversight and AML/CTF from one portal.
Whole-tenant ICT, with Conditional Access across the firm from 23 October 2026.

Defensive and advisory
A Black Shard vCISO is the named owner of your security program: strategy, risk register, policies and board reporting, on a monthly retainer.
Overview
The retainer covers security strategy, risk management, board reporting, policies, incident readiness, supplier assurance and oversight of security projects, including penetration tests, Azure reviews and remediation work, on an agreed cadence.
The scope and meeting cadence are agreed at the start and adjusted as the organisation changes.
Black Shard is an Australian software engineering and cybersecurity firm. The firm builds and operates production systems, among them a law firm's operations portal where every state change lands in an append-only audit ledger, and clinical software that keeps each practice's health data apart in the database itself. The controls a vCISO recommends are drawn from that operating work.
A vCISO, or virtual CISO, is a fractional chief information security officer: a senior practitioner who owns the security program for an agreed share of their time, on a regular cadence. vCISO services cover the work a CISO would own if the organisation employed one.
The usual position is an organisation that has grown past security living in the IT manager's spare hours and has not reached the scale where a full-time executive salary is justified.
Common triggers: a board or insurer has started asking about cyber risk and nobody owns the answer; a large customer has sent a security questionnaire; the business operates in a regulated industry such as health, legal or financial services; or an incident has exposed the gap.
The vCISO vs full-time CISO decision turns on scale. A full-time CISO fits once there is a security team to lead, a threat profile that shifts weekly and a permanent executive seat. Where an organisation grows into that, the strategy, register, policies and board relationship built under the vCISO engagement are documented for the incoming executive to inherit.
The opening months build the parts of the program everything else runs on. A deadline such as a tender, an audit or an insurer renewal can change the order.
The usual first step is a security posture assessment: a gap analysis against the ASD Essential Eight and the CIS Controls. It records where the organisation stands, mapped to recognised controls, and what to fix first.
The findings become the first version of the roadmap, prioritised and costed by effort, so the retainer starts with a plan.
From there the retainer stands up the working parts of the program: the risk register, a policy baseline, an incident response plan and the first board report, with the reporting cadence set for those that follow.
The board report is written for directors who need to question security and decide on it. It is short, it repeats the same structure each period, and it carries the decisions the board is being asked to make.
The standard shape is a monthly retainer. Each session works the same agenda: the risk register reviewed against what has changed, the roadmap moved forward by what was committed last time, and reporting prepared on the board's calendar.
The agenda produces a record a director or auditor can follow month over month.
Between sessions the vCISO handles what arrives outside the cycle: a supplier questionnaire, a board question, an alert that needs a decision. Where the roadmap calls for a penetration test, a secure code review or an Azure tenant review, Black Shard scopes and delivers it as a separate piece of work under the vCISO's oversight.
Everything the retainer produces belongs to the organisation: the strategy, the risk register, the policy set, the incident response plan, the board reports and the library of answered security questionnaires.
Each is kept in the organisation's own systems, so the program does not depend on the retainer continuing and an incoming full-time CISO inherits a working record.
Black Shard also runs penetration testing, Azure security reviews and remediation engineering. Where the roadmap calls for that work, it is scoped separately and overseen by the vCISO who owns the program.
Black Shard holds SMB1001:2026 Gold, issued by CyberCert, has its own estate at Essential Eight Maturity Level 3, assessed September 2026, and operates to the Australian Privacy Principles. Client positions in board reporting and questionnaire responses carry the same distinction between an issued certification and an assessed maturity level.
A monthly CISO services retainer, priced on the size and complexity of the business, the regulatory frame it operates under, the reporting cadence the board needs and how much of the groundwork already exists. A one-off posture assessment is the usual first step.
Across the Australian market, vCISO retainer pricing follows the shape of the engagement, from a light-touch advisory retainer through a working retainer to a full-scope retainer, and cadence is usually the biggest lever on price.
The groundwork that counts is the policies, the risk register and the response plan. A free 30-minute scoping call sets the shape of the retainer, or a brief to info@blackshard.com.au starts it from the detail you have.
Legal
The firm runs intake, conflicts, trust oversight and AML/CTF from one portal.
Whole-tenant ICT, with Conditional Access across the firm from 23 October 2026.

Health
The clinical site and the practice’s ICT now sit with one team.
Hosting, ICT management and security now run under one ongoing engagement.

Property
Every valuation, from inspection to invoice, runs through The Den.
Reports, sketch PDFs and fees come from the same job record in The Den.
Product screens shown with sample data.
Launching 2027
Designed for Australian businesses with 1 to 200 devices.
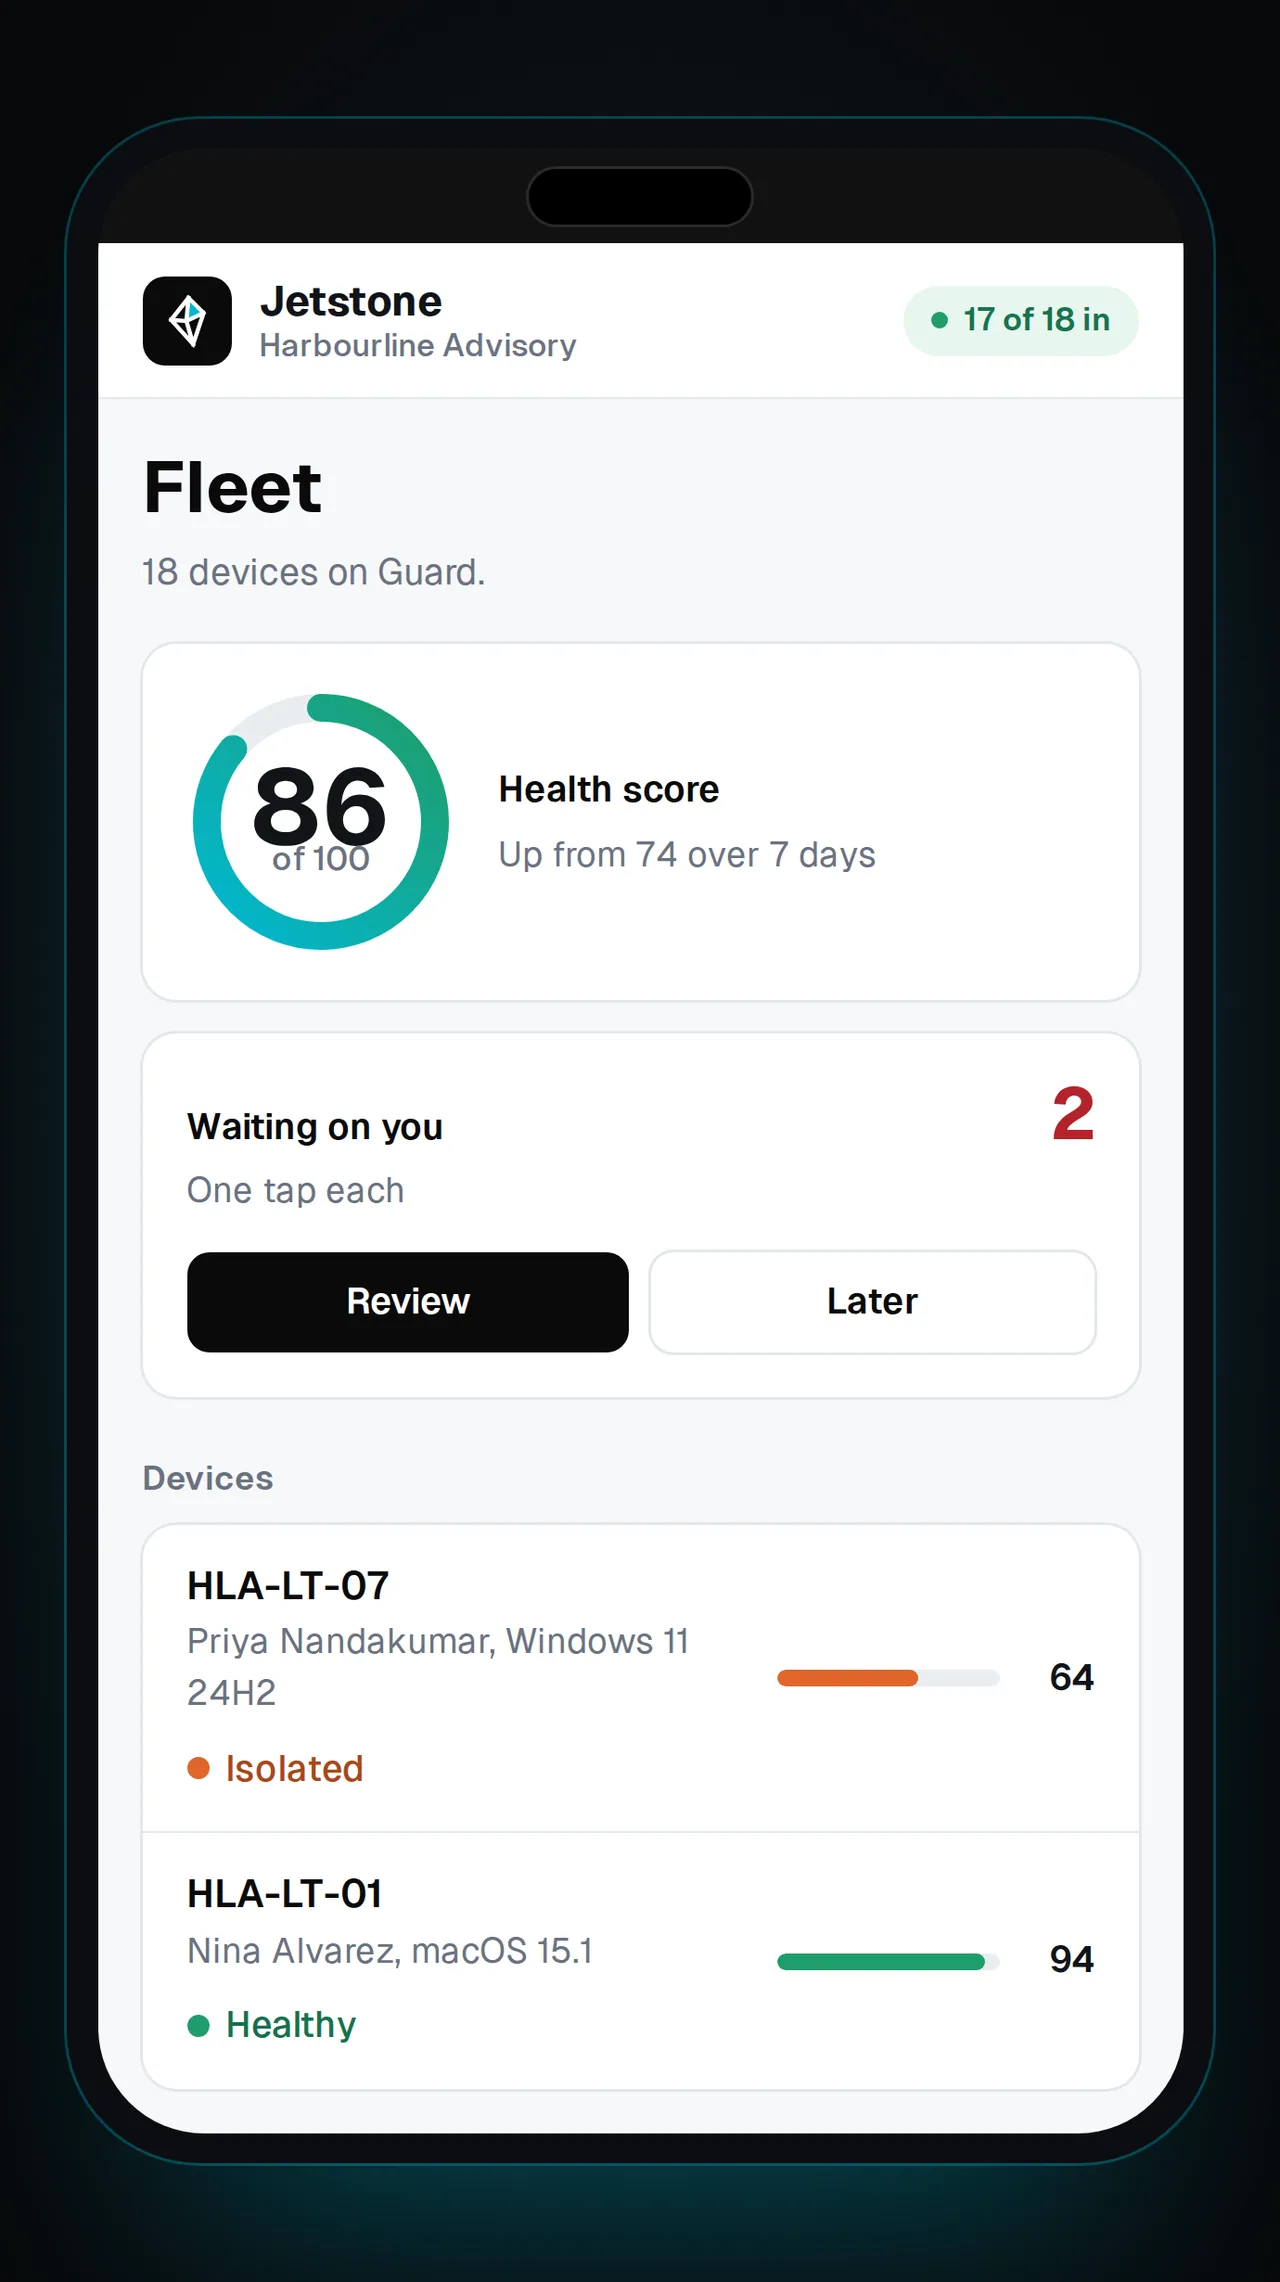
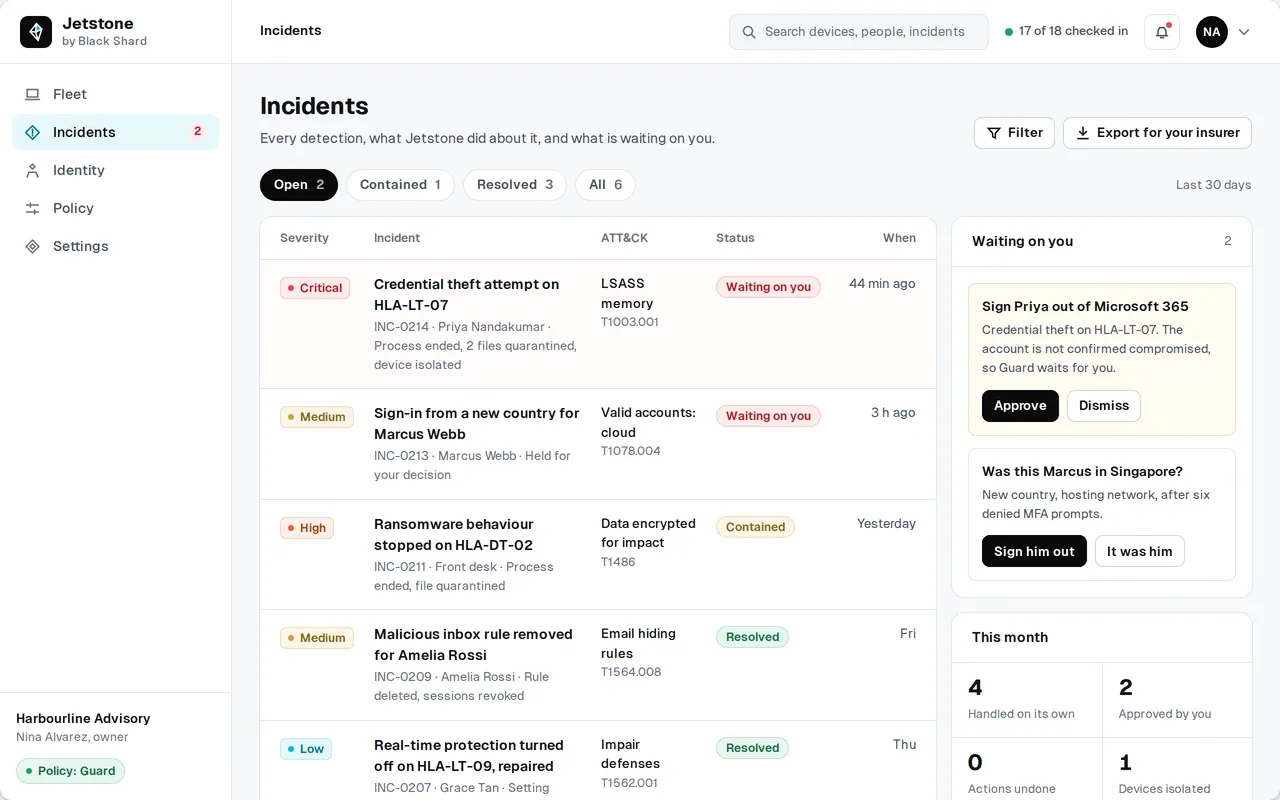
On a high-confidence detection, Jetstone is designed to act on its own against threats on a published list: end the process, quarantine the file, isolate the device, or sign the user out of Microsoft 365 or Google Workspace.
Identity watch will flag impossible travel, MFA fatigue, malicious inbox rules and risky OAuth consents.
Every automatic action will be undoable in one tap.
From the newsroom
Updated Guides
A vCISO, or virtual chief information security officer, is a senior security practitioner who owns an organisation's security program on a part-time or fractional basis. The vCISO sets strategy, keeps the risk register and policies current, reports to the board and leads incident readiness, without the organisation employing a full-time executive.
Security strategy, risk management, board reporting, policies, incident readiness, supplier assurance and oversight of security projects such as penetration tests and Azure reviews. The scope and meeting cadence are agreed at the start and adjusted as the organisation changes.
A CISO services retainer is the standing arrangement a vCISO engagement runs on: an agreed share of a senior practitioner's time on a regular cadence, typically monthly. It covers strategy, policy, the risk register and board reporting, kept current between sessions. Penetration tests and reviews the roadmap calls for are scoped as separate pieces of work.
A full-time CISO is a salaried executive hire. A vCISO retainer provides the same ownership of the security program for a defined fraction of the cost, with the firm's penetration testing, Azure review and engineering capability behind it. An organisation that grows into the full-time role inherits a strategy, register and policy set already built.
On the cadence agreed at the start of the engagement, typically monthly. Between sessions the strategy, policies and register are kept current, and matters that cannot wait for the next session are handled as they arise.
No. Black Shard runs penetration testing, red teaming and phishing simulation as separately scoped engagements. When the vCISO roadmap calls for a test, the firm scopes and delivers it.
Yes. Black Shard is an Australian firm and delivers vCISO engagements Australia-wide. The cadence, reporting and reviews run remotely.
The ASD Essential Eight, the CIS Controls, SMB1001, ISO 27001 and the Australian Privacy Principles. SMB1001 is the one the firm holds a certificate against; the others are frameworks it works against.
The response plan built during the engagement is run, with the vCISO involved in containment decisions, communication and the notification obligations under the Privacy Act's Notifiable Data Breaches scheme. Incident readiness is built early in the engagement so the plan exists before it is needed.
The access the work requires and no more: administrative privilege granted deliberately, reviewed as the engagement changes and removed when it ends.
Book the free 30-minute scoping call or send a brief to info@blackshard.com.au. The usual first step is a security posture assessment, which gives both sides a documented position before a retainer is scoped.