We built the systems GRM LAW runs on.
A legal operations and compliance platform covering intake, conflicts, matter management and trust-account oversight.
- Client
- GRM LAW
- Sector
- Legal
- Connected systems
- Smokeball, Xero
- Releases to the portal
- Weekly
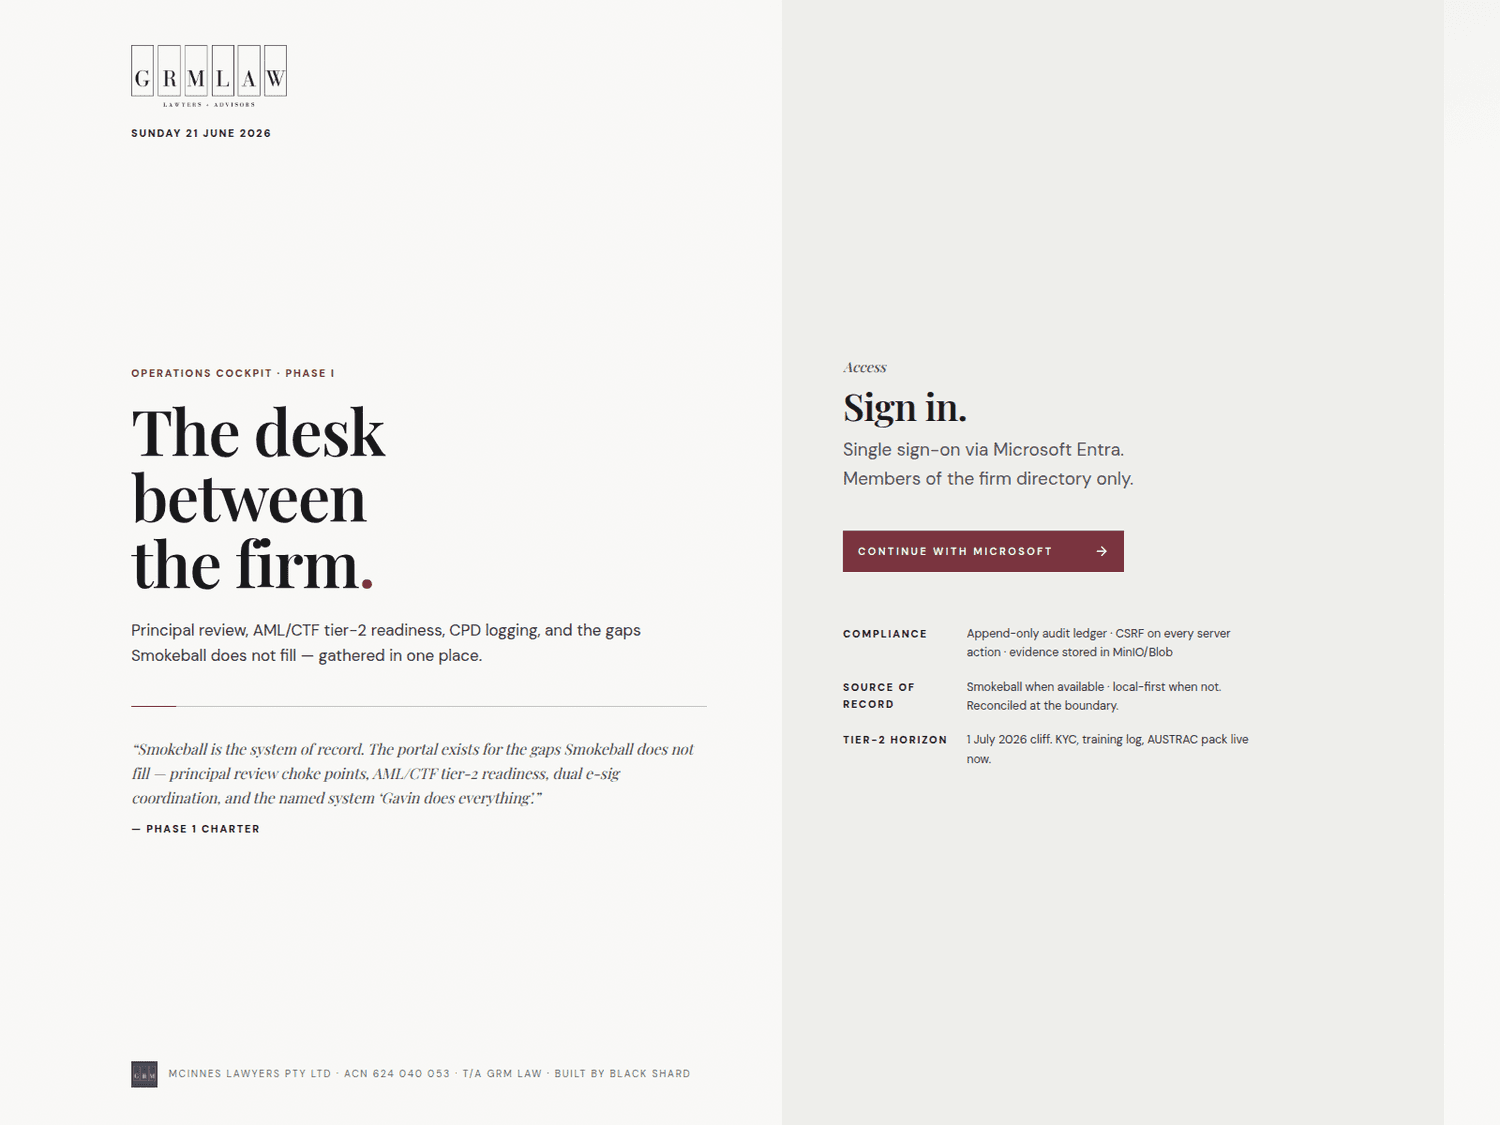
GRM LAW is a law firm. Black Shard built the operations and compliance portal it runs its practice on: a system that sits over Smokeball, holding structured intake, automated conflict search, the matter register, trust-account oversight and the audit trail behind them.
Trust-account controls and access
At the end of each month the portal checks the trust ledger against itself: a trust transaction with no matching matter, one carrying no matter reference at all, and two transactions sharing the same matter, date and amount all raise a named exception before the close is signed off. A change to a trust-account payee's bank details needs a second approver and a step-up code from an authenticator app, then a 24-hour cooling-off period before it takes effect. Every one of those events lands on an audit ledger that is append-only at the database itself: a trigger rejects an update or delete outright, even from a credential that holds table-level privileges.
Role-based access sits behind a hardened content-security policy, staff sign in through TOTP, and the firm's external auditor can be handed read-only reach to the ledger export without touching anything else in the portal. The firm also runs a Windows desktop client whose updates are checksum-verified before they install. We ship to the portal weekly under an ongoing engagement; the build evolves with the workflow.
What we built.
- Compliance and operations portal: structured intake, automated conflict search, the matter register
- Trust-account oversight: end-of-month exception detection for orphan, unbound and duplicate trust transactions
- Dual control, a TOTP step-up and a 24-hour cooling-off period on every change to a trust-account payee's bank details
- An append-only audit ledger enforced at the database itself, with read-only export access for the firm's external auditor
How it is secured.
Role-based access over a hardened content-security policy, TOTP sign-in, an append-only audit ledger enforced at the database itself, and read-only ledger access for the firm's external auditor.
Services involved.
Start an engagement.
Tell us what you need built, reviewed or secured.