At a glance
Read-only
Global Reader, removed at the end

Defensive and advisory
A review of the Entra ID and Microsoft 365 tenant your organisation signs in to: conditional access, privileged roles, app consent and offboarding.
Fixed scope
Microsoft 365 and Azure security review
Fixed scope, priced before the work starts.
Findings and a remediation plan.
At a glance
Global Reader, removed at the end
At a glance
CyberCert public registry
Overview
Conditional access coverage is checked across every account that matters, including the break-glass accounts that exist for when everything else fails. Recovery readiness is part of the review, so a lost administrator account cannot lock the business out.
Black Shard is an Australian software engineering and cybersecurity firm. Most Australian organisations run identity through Microsoft Entra ID and Microsoft 365, where a compromised password, an over-permissioned application or a missed offboarding step gives an attacker a valid sign-in.
Black Shard operates Azure and Microsoft 365 tenants in production for its own systems and for client organisations. Findings are manually verified before they are reported, and the remediation plan is tied to controls already in the Microsoft 365 licence.
Six areas, each checked against how the tenant is used.
Conditional access and multi-factor authentication coverage is checked across every account that matters, including the break-glass accounts that exist for when everything else fails and are often left unmonitored or unprotected.
Privileged roles are audited in full: who holds Global Administrator and the other high-impact roles, whether each assignment is still justified, and whether access is standing or granted just in time.
App consent is reviewed the same way: which third-party and internal applications users have granted access to the tenant, what permissions those grants carry, and whether any are broad enough that a single phishing click becomes a mailbox-wide compromise. Offboarding closes the loop: whether a departing user's access is removed on the day they leave, and whether the tenant can be recovered if an administrator account is lost. For an organisation on Microsoft 365, valid credentials or a consented application reach mailbox rules, file shares and Teams conversations directly, which is why these controls carry the weight they do.
The Microsoft 365 and Azure security review covers identity as one area alongside privilege, networking, secrets, logging and workload configuration, and for many tenants that depth is sufficient.
The Entra ID review examines the Microsoft 365 identity estate on its own: every conditional access policy, every privileged role, every app consent, and the offboarding and recovery processes around them.
If it is unclear which fits, say so in the brief and we will recommend the scope.
The review needs read access to the tenant, a brief on what the organisation runs on Microsoft 365, and time with the people who can answer the questions a configuration export cannot. Scoping and the debrief run by video call wherever you are based.
Access is reader-level and scoped to the engagement: typically Global Reader in Entra ID with read access to Conditional Access policies and Enterprise Applications, agreed at scoping and removed when the review ends. Black Shard holds SMB1001:2026 Gold, issued by CyberCert. Organisations in Brisbane that would rather scope and debrief across a table have that option.
A Microsoft 365 and Azure security review runs to a fixed scope, priced before the work starts, with written findings and a remediation plan.
Effort is driven by the size of the identity estate: how many users, guest accounts and privileged roles the tenant carries, and how many third-party applications have accumulated access over the years.
The engagement runs with a defined target, timeframe and deliverable agreed before work starts, on a free 30-minute scoping call or from a brief to info@blackshard.com.au with the rough shape of the tenant.

Legal
The firm runs intake, conflicts, trust oversight and AML/CTF from one portal.
Whole-tenant ICT, with Conditional Access across the firm from 23 October 2026.

Health
The clinical site and the practice’s ICT now sit with one team.
Hosting, ICT management and security now run under one ongoing engagement.

Property
Every valuation, from inspection to invoice, runs through The Den.
Reports, sketch PDFs and fees come from the same job record in The Den.
Product screens shown with sample data.
Launching 2027
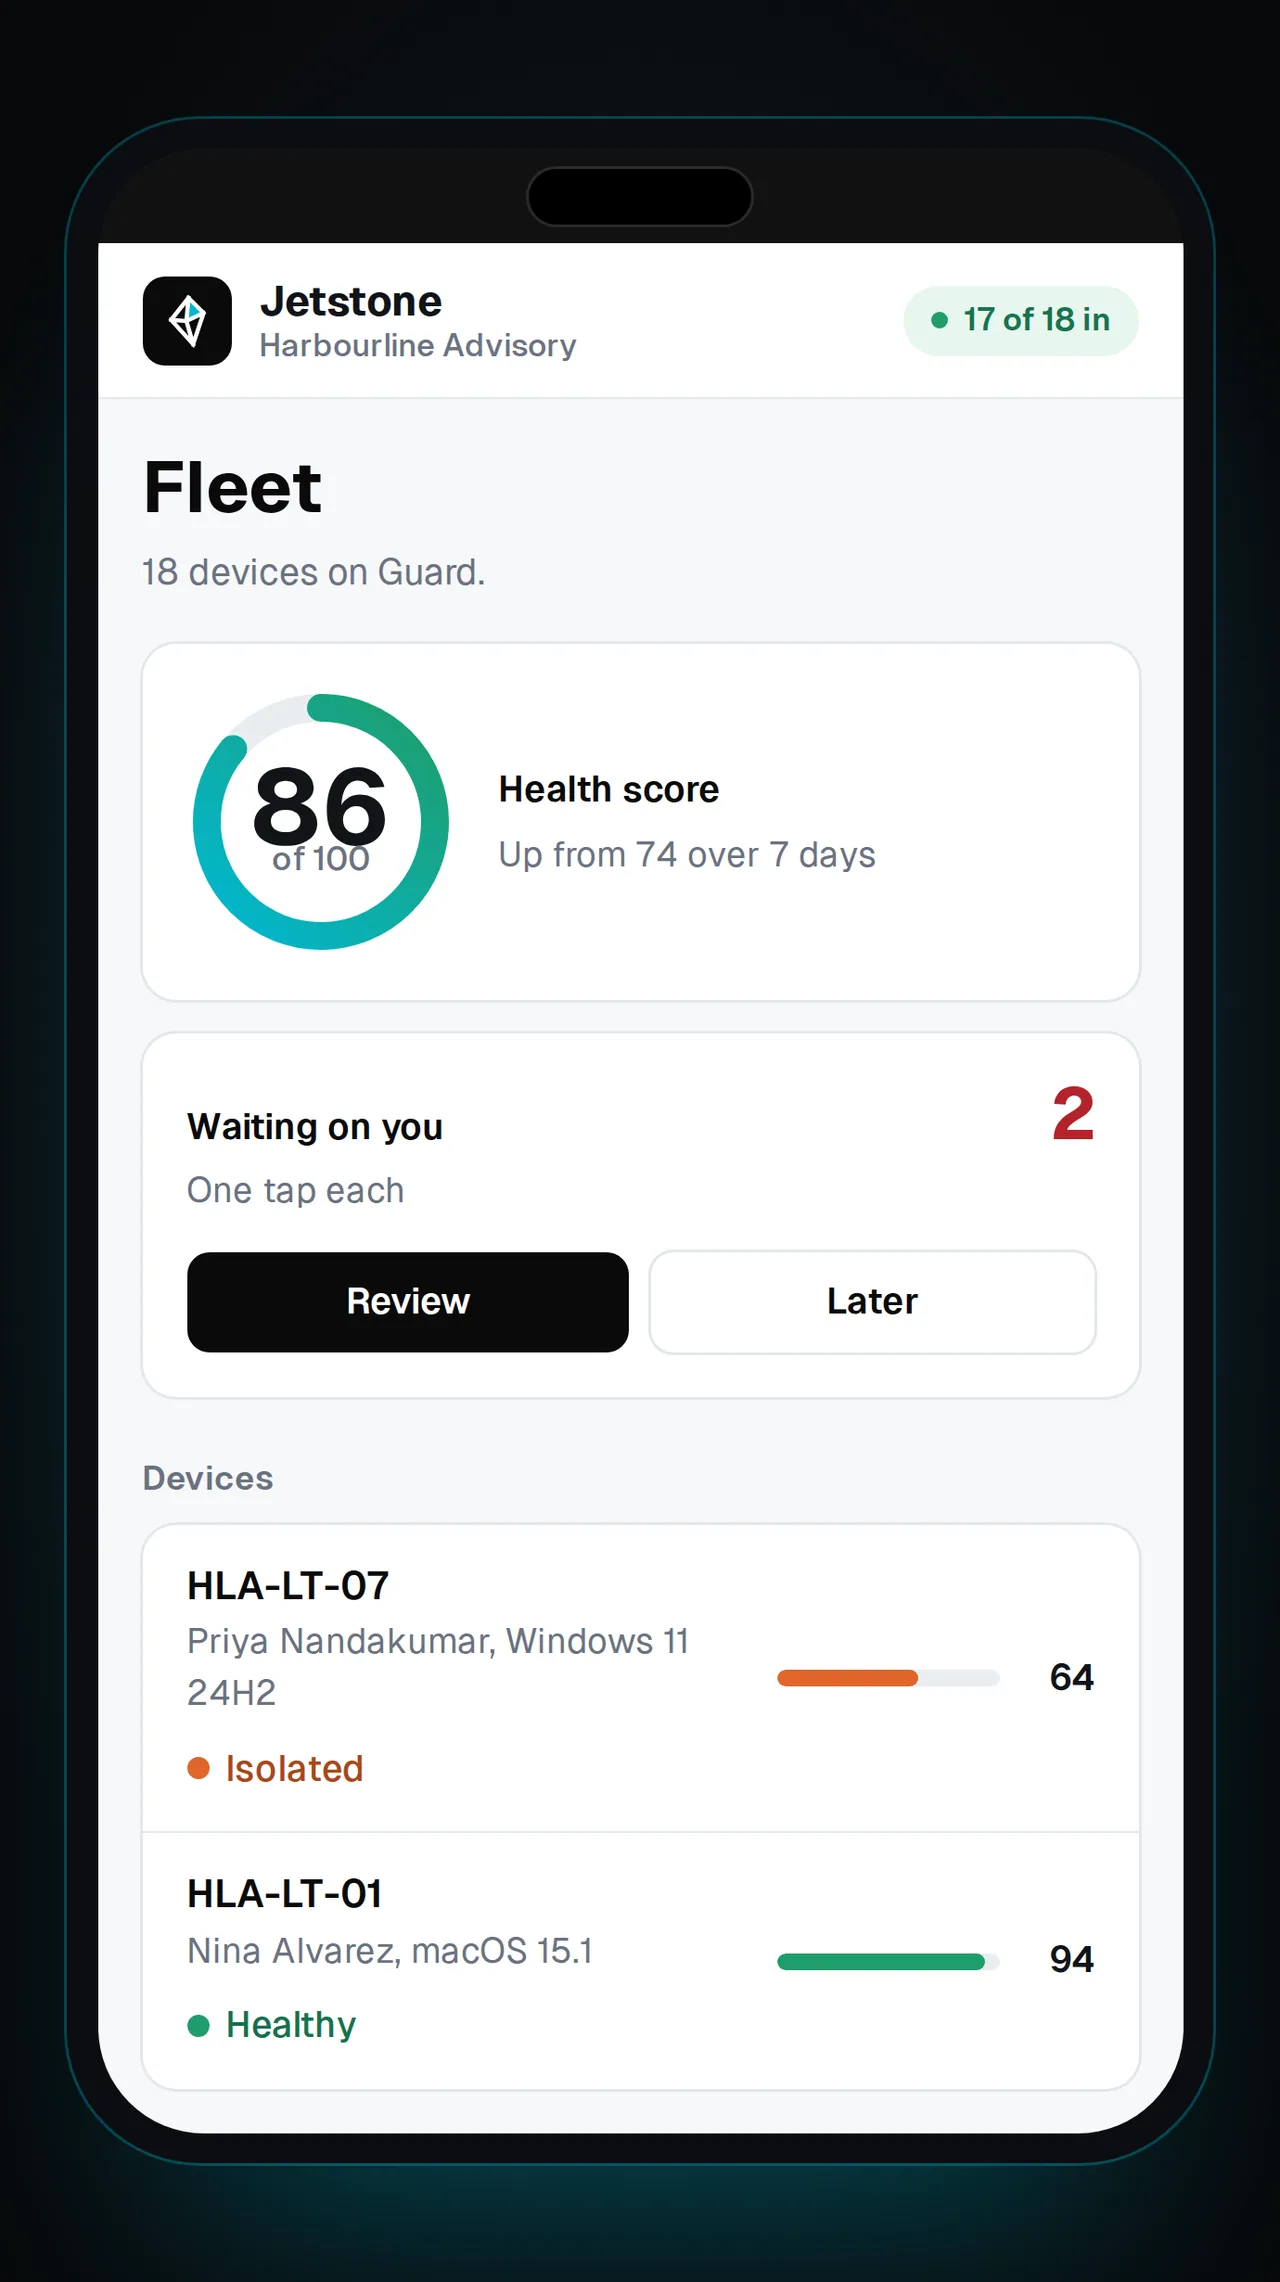
Designed for Australian businesses with 1 to 200 devices.
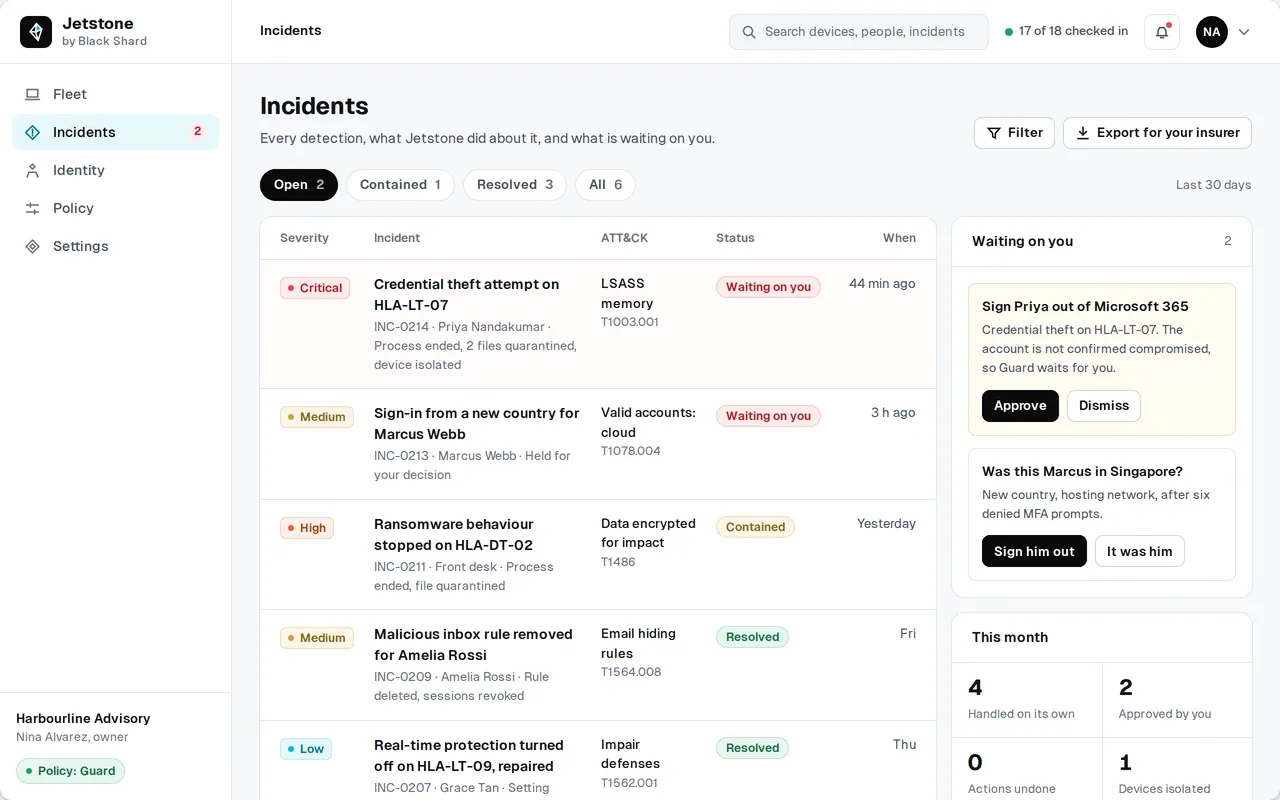
On a high-confidence detection, Jetstone is designed to act on its own against threats on a published list: end the process, quarantine the file, isolate the device, or sign the user out of Microsoft 365 or Google Workspace.
Identity watch will flag impossible travel, MFA fatigue, malicious inbox rules and risky OAuth consents.
Every automatic action will be undoable in one tap.
From the newsroom
Updated Guides
 High severity
Reader-level roles scoped to the review, typically Global Reader in Entra ID with read access to Conditional Access policies and Enterprise Applications, agreed at scoping and removed when the engagement ends.
No, though they overlap. The Azure review covers identity as one area across the whole tenant. This review goes deeper into Entra ID and Microsoft 365: conditional access, privileged roles, app consent and offboarding. Describe the situation in the brief and we will recommend the scope.
Yes. Black Shard is a software engineering firm as well as a cybersecurity firm, so remediation can run as advisory support or hands-on configuration change after the review. The plan is written so your own team can execute it.
It runs as a fixed-scope engagement, with the target, timeframe and deliverable agreed before work starts. The size of the identity estate (users, guest accounts, privileged roles and app consents) drives the effort.
Yes. Break-glass accounts exist for when everything else fails, which makes them among the most consequential accounts in a tenant. We check whether they exist, how they are protected, and whether anyone would notice if one were used.
Yes. Black Shard is an Australian firm and delivers Australia-wide. Scoping and the debrief run remotely as standard, and organisations in Brisbane can choose an in-person debrief.