Essential Eight
The maturity level a tender or an insurer names, rated strategy by strategy.

Compliance deadline
We identify which requirements are met, which are partial and which need work, then sequence the remediation against the assessment date and collect the evidence as each control lands.
Compliance deadline
Readiness work for any security or privacy framework, from the Essential Eight and SMB1001 to privacy obligations.
The maturity level a tender or an insurer names, rated strategy by strategy.
A certifiable standard with tiers, and an entry on the CyberCert public register once issued.
Scope, gap analysis against Annex A and the documentation an auditor expects.
A data map, a gap review against the Australian Privacy Principles and the disclosures due from 10 December 2026.
Risk assessment, policy design and compliance testing, reported in writing to the governing body.
AI governance groundwork and a Voluntary AI Safety Standard assessment.
How it works
A defined program with milestones toward the certification or audit date.
Current position
Every requirement checked against the environment as it runs and recorded as met, partial or missing.
Sequenced remediation
Gaps closed in order of risk against the assessment date, hands-on where you want it.
Evidence as you go
Evidence collected as each control is implemented, so the position is on the record before the date.
Assessment support
A finished pack for the attestation or the auditor, and answers to their technical questions.
Services
Maturity assessed against all eight controls, a written report and an uplift plan.
From A$5,950ex GSTGap assessment against your target tier, evidence pack, remediation plan and support through certification.
From A$3,950ex GSTIdentity, Conditional Access and tenant settings, with written findings and a remediation plan.
From A$3,500ex GSTA security lead on a regular cadence who owns the program and reports on it to the board.
On the record
Our own certificate and maturity level sit on the record, and an ISO/IEC 27001:2022 Lead Auditor leads security.
16 Jun 2026 to 17 Jun 2027
VerifySMB1001:2026 Gold, opens in a new tabMaturity Level 3, assessed September 2026.
Kane Roberts, Director and Chief Information Security Officer, holds the Exemplar Global Lead Auditor credential for ISO/IEC 27001:2022 (certificate C-560291).
Personal credential

Property
Off-market deal sourcing and the AML/CTF program run from one staff app.
Screening runs against 11,414 DFAT Consolidated List rows every day.

Financial services
Staff, investors and the board work from one portal inside the licence perimeter.
Every investor is identity-checked through InfoTrack before they can proceed.

Legal
The firm runs intake, conflicts, trust oversight and AML/CTF from one portal.
A new release of the portal ships every week.
Launching 2027
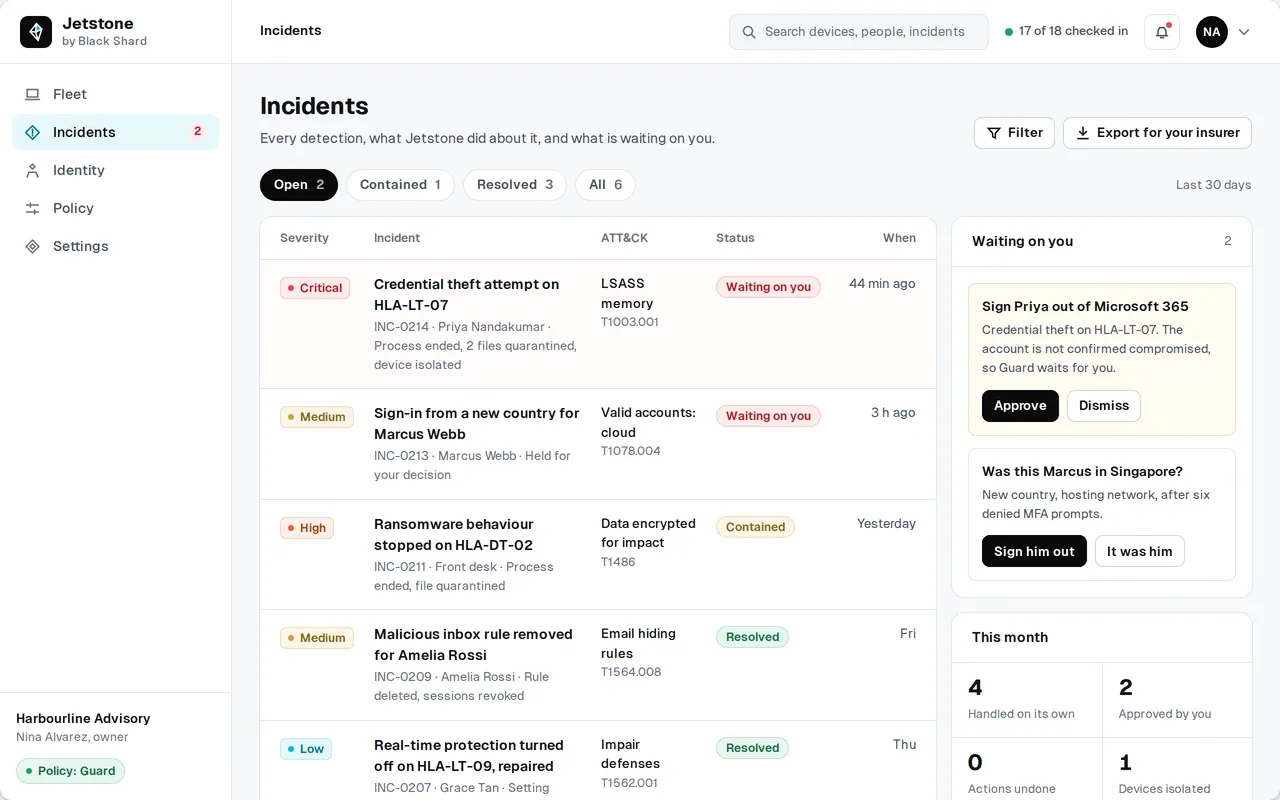
Designed for Australian businesses with 1 to 200 devices.
On a high-confidence detection, Jetstone is designed to act on its own against threats on a published list: end the process, quarantine the file, isolate the device, or sign the user out of Microsoft 365 or Google Workspace.
Identity watch will flag impossible travel, MFA fatigue, malicious inbox rules and risky OAuth consents.
Every automatic action will be undoable in one tap.
Reading
Policy and regulation
The gap-closing work sets the timeline. A business already running most of the controls can be ready as soon as the evidence is assembled; one starting from nothing needs a program that runs to the date.
Both. Our engineers do the hands-on work where you want it, or hand your IT provider a plan precise enough to execute and verify each milestone.
The one being asked for. Where nobody has named one, the Essential Eight and SMB1001 overlap heavily, so work done for one counts toward the other.
No. CyberCert issues SMB1001 certificates, an accredited certification body issues ISO 27001, and the ASD certifies nobody against the Essential Eight. We get the controls working and the evidence ready.
Go deeper
Under attack
Tender readiness
Secure build
We come back with the gap, the sequence and a fixed scope.