Software engineering
Web, mobile and platform builds, run in production.

Secure build
Threat modelling at design, access control and secrets handled in the architecture, security gates in the pipeline, and an independent review before higher-risk systems ship.
Secure build
Security is part of the engineering work, from the design review to the release gate.
How it works
Fixed-scope or ongoing, depending on whether the requirement is a defined build or a product that needs continuous development.
Discovery and design
The tasks the product performs, the data it holds and the threat model behind it.
Build
Product design, engineering and the delivery pipeline, with tenant isolation enforced in the database.
Review
Secure code review and a test of higher-risk systems before release.
Run
Hosting, monitoring and continued development after launch, in Australian regions.
Services
Web, mobile and platform builds, run in production.
Authentication, authorisation, injection, secrets, dependencies and business logic.
Landing zones, managed hosting and delivery pipelines in Australian regions.
Applications and APIs tested before release, with a re-test of agreed fixes.
From A$4,950ex GSTOn the record
The same discipline runs every system we build, host and secure.

Health
Specialists run notes, letters, orders and billing from one app.
A new version reaches specialists on the App Store, Google Play and the web every week.

Property
Every valuation, from inspection to invoice, runs through The Den.
Valuers book, inspect, value and invoice every job in The Den.

Legal
The firm runs intake, conflicts, trust oversight and AML/CTF from one portal.
A new release of the portal ships every week.
Launching 2027
Designed for Australian businesses with 1 to 200 devices.
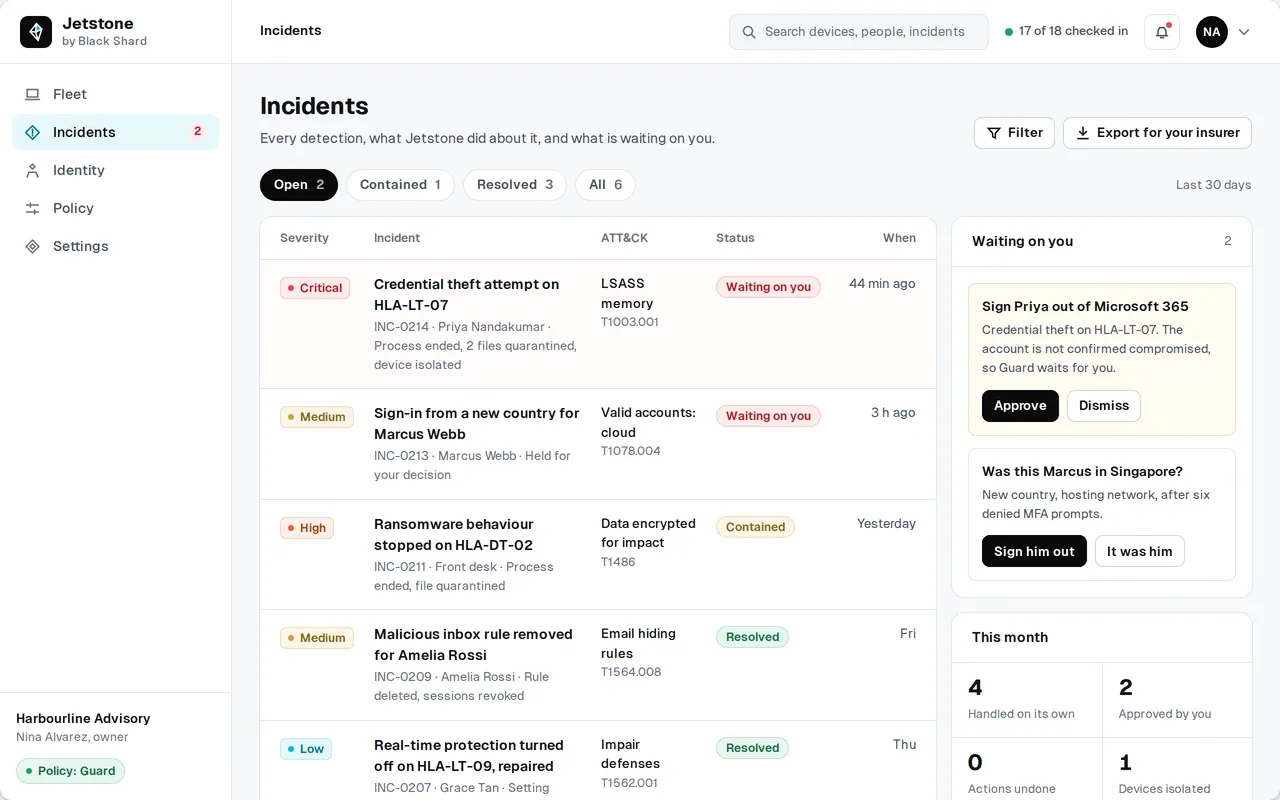
On a high-confidence detection, Jetstone is designed to act on its own against threats on a published list: end the process, quarantine the file, isolate the device, or sign the user out of Microsoft 365 or Google Workspace.
Identity watch will flag impossible travel, MFA fatigue, malicious inbox rules and risky OAuth consents.
Every automatic action will be undoable in one tap.
Reading
 Critical severity
 High severity
Third-party assurance on a platform Black Shard built is run by a separate reviewer with no part in the build.
Where you want us to. Workloads run on dedicated infrastructure in Azure Australian regions, patched, backed up, monitored and reported on every month.
Yes. A secure code review or threat model runs as a standalone engagement, with findings written for the engineers who will fix them.
Guardrails, an audit trail and tenant isolation are designed in from the start, the same controls we run in our own AI pipelines in production.
Go deeper
Under attack
Compliance deadline
Tender readiness
A director reads every brief and comes back with a scope.